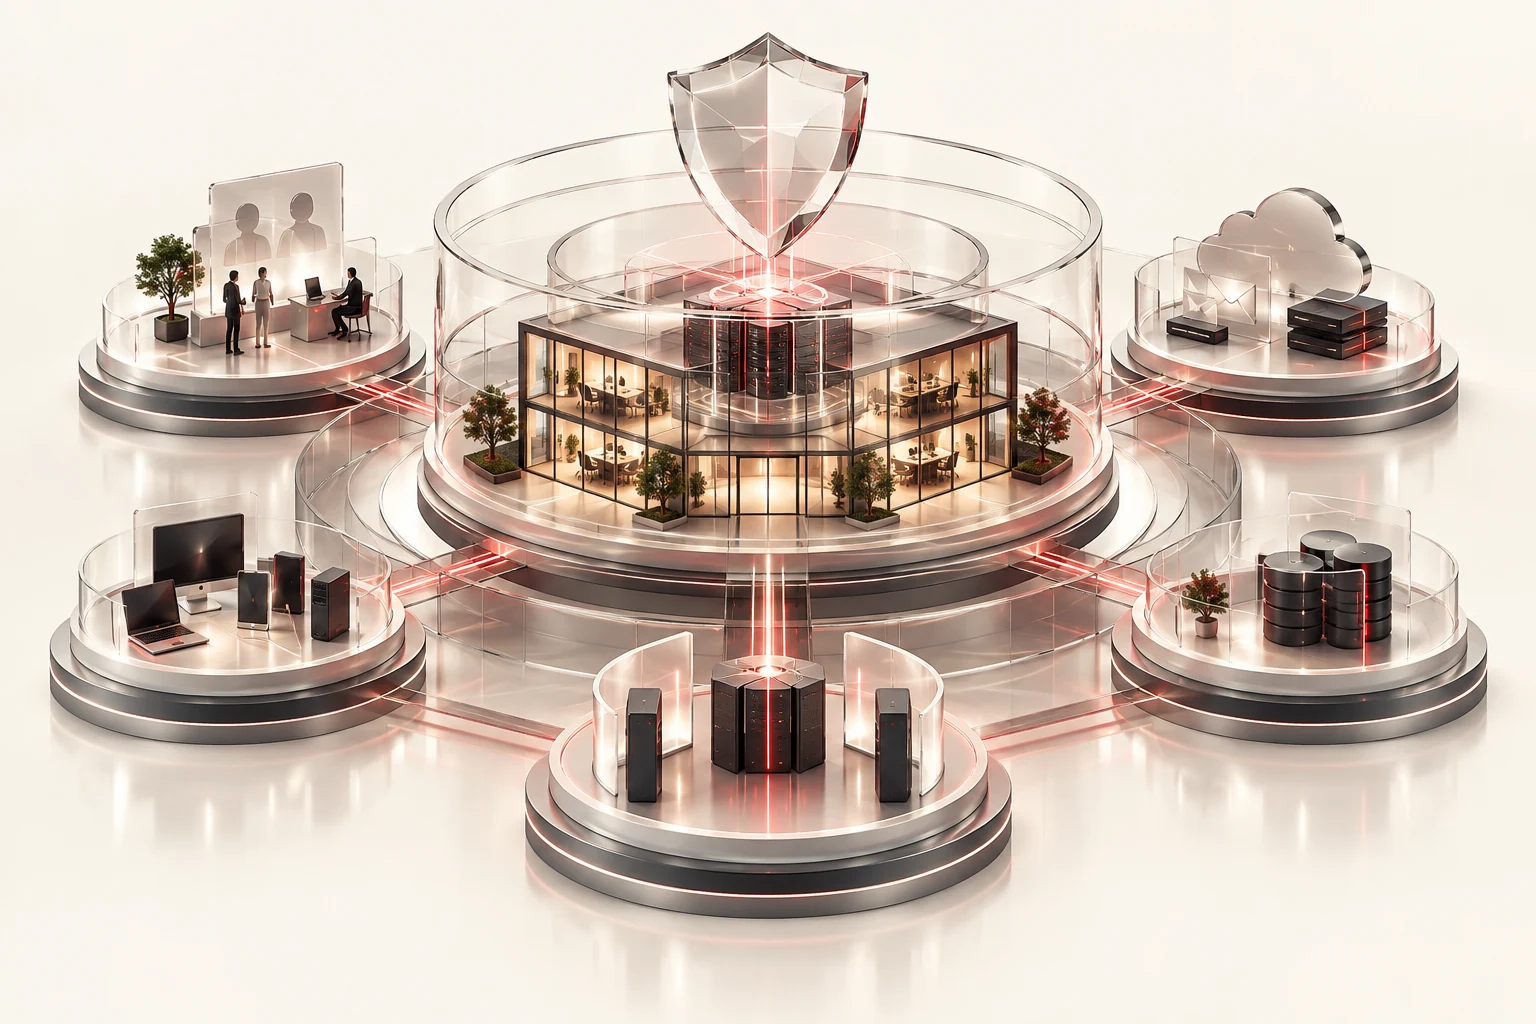
Connect protection across accounts, devices, networks, and data.
02
Prioritize the right fixes
Focus corrective work around business impact and exposure.
03
Prepare a coordinated response
Know how security and recovery responsibilities fit together.
WHAT THIS LOOKS LIKE FOR YOUR BUSINESS
Protect the layers. Connect the response.
Security goes beyond installing a tool. We bring Sophos and SentinelOne capabilities together with access, configuration, recovery, vendor coordination, and accountable operating practices.
Explore a situation. See how the work connects.
SERVICE IN ACTIONIllustrative workflow
Connect the security signal to the right response.
Signal
An agreed control identifies suspicious activity.
Assessment
Review context and potential business impact.
Coordinated action
Apply authorized response and recovery steps.
What we own
We define tool coverage, response authority, provider roles, and escalation before an incident.
A response model your business can understand and review.
Bring the supplier into the security conversation.
Map the relationship
Identify the information and service involved.
Review obligations
Coordinate safeguards and applicable agreements.
Track ownership
Record decisions, missing items, and follow-up.
What we own
We organize technical findings and BAA coordination with your authorized compliance reviewers.
Visible responsibilities across your business and its suppliers.
CAPABILITY WITH CLEAR OWNERSHIP
Protection across the places your business works.
Connect endpoint tools, identity, email, networks, cloud, and recovery into a coordinated security operation.
01 / SERVICE AREA
Protect people & devices
Safer accounts, endpoints, and everyday decisions.
Sophos / SentinelOne endpoint protection
Identity, MFA & access reviews
Policies and security awareness
Scope & technical details
People & policies
Help your people recognize suspicious activity and use business technology consistently.
Security awareness and phishing-readiness guidance
Practical policies for acceptable use, reporting, and sensitive information
Onboarding, role-change, and offboarding procedures
Identity & access
Protect the accounts and privileges that connect people to your systems and data.
Multifactor authentication and secure sign-in policies
Access reviews, least privilege, and administrator account controls
Joiner, mover, and leaver access changes with accountable owners
Endpoints & servers
Connect endpoint protection, configuration, updates, and detection across supported workstations and server workloads.
Sophos or SentinelOne deployment and policy management as scoped
Endpoint detection and response (EDR), alert routing, and approved containment
Hardening, patch priorities, encryption settings, and protection-health reviews
02 / SERVICE AREA
Secure the connections
Email, networks, cloud, applications, and data.
Email & collaboration safeguards
Network, firewall & remote-access controls
Cloud, application & data permissions
Scope & technical details
Email & collaboration
Reduce exposure through business email, shared files, and the collaboration tools your team uses.
Email protection, phishing controls, and mailbox security settings
Microsoft 365 or Google Workspace sharing and access reviews
Domain-authentication coordination and response to suspicious mailbox activity
Networks & remote access
Manage the boundaries and connections between users, locations, cloud services, and important systems.
Firewall policies, secure remote access, and network segmentation
Wireless, switching, and device-configuration reviews
Supported network security signals, updates, and configuration backups
Cloud, applications & data
Bring cloud configuration, application access, integrations, and information handling into the security plan.
Tenant and workload configuration reviews
Data access, sharing, retention, and protection requirements
Application, integration, and AI-tool permissions and supplier dependencies
03 / SERVICE AREA
Prepare for incidents
Recovery and response with named owners.
Incident contacts & response ownership
Backup and recovery coordination
Physical-safeguard handoffs
Scope & technical details
Physical safeguards
Coordinate the physical practices that affect the security of devices, facilities, and information.
Workstation, server-room, and equipment-access considerations
Device custody, remote-work practices, and secure disposal coordination
Technical dependencies with facilities and designated physical-security owners
Backup & resilience
Connect protected copies, recovery priorities, and incident readiness to the systems that matter most.
Backup scope, access separation, and retention requirements
Restore testing and recovery-runbook coordination
Business-impact priorities, recovery dependencies, and continuity exercises
Response coordination
Agree alert review, containment authority, escalation contacts, and business recovery responsibilities.
04 / SERVICE AREA
Connect compliance work
BAAs, vendor responsibilities, and organized evidence.
Vendor inventory & BAA coordination
Compliance evidence and open actions
Risk reviews and improvement planning
Scope & technical details
Vendors & governance
Make supplier responsibilities, compliance needs, and business decisions visible parts of the security operation.
Vendor inventory, due diligence, and applicable BAA coordination
Requirement-to-control mapping and evidence organization
Risk ownership, exception reviews, and security roadmap priorities
Map the relationships
Identify suppliers and subcontractor relationships that may handle protected health information. Confirm roles with your privacy or compliance owner.
Gather the agreements
Request applicable BAAs and relevant provider terms. Record the contracting entity, services covered, agreement status, and missing information.
Coordinate review
Route scope, safeguards, incident-reporting terms, subcontractor responsibilities, and contract questions to your authorized reviewers.
Maintain the record
Track executed copies and outstanding items. Revisit the register when services, suppliers, data handling, or contractual arrangements change.
Tools, coverage hours, response authority, and compliance responsibilities are agreed for your environment. Technology supports an ongoing security and compliance program.
THE LOGIC NETWORKS DIFFERENCE
A security partner who sees the whole picture.
Your people should know whom to call when something feels wrong. We connect Sophos and SentinelOne capabilities with practical safeguards, response responsibilities, and supplier follow-through.
They provide selected protection capabilities. We connect them with identity, email, network, cloud, recovery, and governance controls. Product, licensing, response coverage, and responsibilities are confirmed in scope.
How is the service scoped?
Tools, coverage hours, response authority, and compliance responsibilities are agreed for your environment. Technology supports an ongoing security and compliance program.
What happens in the consultation?
Tell us what concerns you most. We’ll help turn it into practical security priorities. We discuss priorities, identify what needs discovery, and agree a useful next step. Any assessment, proposal, or implementation scope is confirmed together.
LET’S PUT OUR HEADS TOGETHER
A conversation about your business.
01Current protection and recent concerns
02Sensitive data and critical accounts
03Incident contacts and compliance needs
Bring what you know. We’ll work through the rest with you.
YOUR NEXT STEP
Let’s talk through your security priorities.
Tell us what concerns you most. We’ll help turn it into practical security priorities.